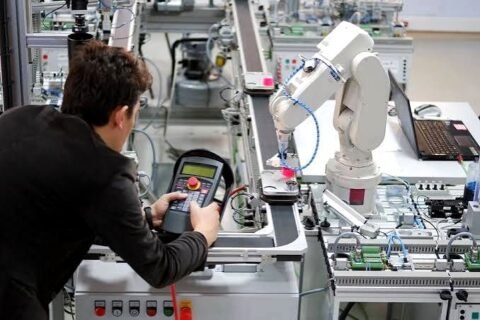
Industrial automation is entering a new phase as manufacturers integrate artificial intelligence, edge computing, and connected control systems. However, these capabilities introduce new demands for cybersecurity, system reliability, and predictable execution.
Traditional PLC and DCS architectures continue to support critical industrial operations. Meanwhile, high-performance processors and system-on-chip (SoC) platforms enable advanced computing within industrial environments.
The challenge lies in combining these technologies without compromising operational continuity. Therefore, manufacturers need resilient software foundations that protect critical workloads, isolate faults, and support long-term system maintenance.
Industrial Automation Evolution: From PLC Controllers to MPU-Based Architectures
For decades, programmable logic controllers (PLCs) and microcontrollers have provided predictable control across manufacturing plants, energy facilities, and process industries.
These platforms execute established control logic, process field signals, and coordinate industrial equipment. Their deterministic behavior remains fundamental to modern factory automation.
However, industrial applications increasingly require capabilities beyond conventional controller architectures. Machine vision, advanced human-machine interfaces (HMIs), edge analytics, and artificial intelligence demand greater processing capacity.
Consequently, manufacturers are adopting microprocessor units (MPUs) and system-on-chip platforms alongside existing controllers.
This transition does not require replacing every established PLC or distributed control system (DCS). Instead, manufacturers can introduce additional computing resources while preserving proven control infrastructure.
A combined PLC-plus-MPU architecture allows each platform to handle appropriate workloads. PLCs maintain field-level control, while MPUs support visualization, analytics, connectivity, and AI applications.
This approach also provides a practical pathway toward software-defined industrial automation.
Mixed-Criticality Computing: Balancing Real-Time Control and AI Workloads
Industrial systems increasingly execute applications with different performance and safety requirements on shared computing platforms.
For example, a modern automation system may run deterministic control tasks alongside visualization, predictive maintenance, and machine learning applications.
These workloads do not share identical timing requirements. Hard real-time control requires predictable execution, while analytics applications may tolerate variable processing delays.
However, resource-intensive workloads can interfere with critical functions without proper system isolation.
Therefore, industrial computing platforms must manage mixed-criticality workloads through controlled resource allocation and execution boundaries.
A resilient architecture should address three fundamental requirements:
- Temporal isolation: Prevent lower-priority applications from disrupting critical task execution.
- Spatial isolation: Protect memory and system resources between independent software components.
- Fault containment: Restrict software failures or compromised processes to their designated execution environments.
Moreover, predictable scheduling and controlled recovery help maintain operational continuity.
These capabilities become particularly important when manufacturers consolidate multiple applications onto fewer computing platforms.
Microkernel Architecture: Strengthening Industrial System Resilience
A microkernel operating system provides one architectural approach to improving software isolation and fault management.
Unlike architectures that place numerous services inside the kernel, microkernel designs keep the core operating system relatively small. They move many services into separate processes.
This separation can reduce the impact of individual software failures. It also supports clearer boundaries between critical functions and supporting applications.
For industrial automation, these characteristics provide several potential benefits.
First, process isolation helps prevent defective applications from directly affecting unrelated workloads. Second, controlled communication between components supports structured system design.
Furthermore, developers can implement recovery mechanisms for selected services without necessarily restarting the entire application environment.
However, microkernel architecture alone does not guarantee system safety or cybersecurity. Engineers must also consider hardware protection, software configuration, secure development practices, and lifecycle maintenance.
QNX OS and Secure Industrial Automation Development
QNX provides a microkernel-based operating system platform for embedded and mission-critical applications.
Its architecture supports process isolation, controlled resource access, and real-time execution. These capabilities make it relevant to industrial platforms that combine control-related functions with higher-level computing workloads.
As manufacturers introduce MPUs and SoCs into industrial equipment, operating-system architecture becomes an important design consideration.
A suitable software foundation must support predictable execution while accommodating visualization, connectivity, and analytics.
QNX can serve as one foundation for these applications. Nevertheless, engineering teams must validate its suitability against specific hardware, performance requirements, safety objectives, and cybersecurity requirements.
The broader industry trend is clear: industrial software platforms increasingly influence system architecture, maintainability, and lifecycle management.
Industrial Cybersecurity: Integrating Protection Throughout the System Lifecycle
Industrial cybersecurity requires more than adding security features before deployment.
Connected automation platforms introduce additional software dependencies, communication interfaces, and potential attack surfaces.
Therefore, manufacturers should incorporate security considerations during architecture definition, software development, integration, and maintenance.
A comprehensive approach should address:
- Memory protection: Restrict unauthorized access between software components.
- Process isolation: Limit the potential impact of defective or compromised applications.
- Secure communication: Protect data exchanged between controllers, supervisory applications, and external systems.
- Software maintenance: Establish procedures for vulnerability assessment, updates, and lifecycle support.
- Recovery planning: Define how systems respond to software faults while maintaining critical operations.
Standards such as IEC 62443 provide a framework for industrial automation and control system cybersecurity.
Meanwhile, IEC 61508 addresses functional safety principles for electrical, electronic, and programmable electronic safety-related systems.
These standards address different engineering objectives. Consequently, manufacturers should evaluate cybersecurity and functional safety requirements independently while coordinating their implementation.
Modernizing Legacy Control Systems Without Disrupting Operations
Industrial modernization rarely begins with a completely new installation.
Many factories operate PLCs, DCS platforms, and specialized control equipment that remain integrated into established production processes.
Replacing these systems can introduce engineering costs, commissioning risks, and operational interruptions.
A gradual modernization strategy can reduce these challenges.
For example, manufacturers can retain existing PLCs for deterministic field control while introducing MPU-based platforms for advanced visualization and analytics.
This architecture allows new applications to access relevant operational data without requiring immediate replacement of established control infrastructure.
Moreover, engineers can introduce predictive maintenance, machine vision, and edge computing through carefully scoped integration projects.
However, each implementation requires compatibility testing, network segmentation, resource planning, and defined recovery procedures.
In practice, successful modernization depends on preserving control-system stability while introducing new capabilities incrementally.
Industrial Applications: Where Resilient Computing Architectures Add Value
Resilient software foundations support several emerging industrial applications.
Smart Manufacturing and Factory Automation
Manufacturers can combine PLC-based machine control with MPU-powered vision systems, production analytics, and advanced HMIs.
Process isolation helps separate critical control functions from applications with variable computing demands.
Process Automation and DCS Integration
Process plants can introduce additional supervisory applications while maintaining established control strategies.
Engineers should define communication boundaries between DCS controllers, edge platforms, and enterprise systems.
Robotics and Physical AI
Industrial robots increasingly combine motion control, perception, and computationally intensive algorithms.
A structured software architecture can help separate time-sensitive control functions from higher-level perception and planning workloads.
Energy and Infrastructure Systems
Power generation, electrical distribution, and infrastructure applications require predictable operation and controlled fault responses.
Engineers should evaluate computing architecture alongside system availability, cybersecurity, and applicable safety requirements.
Engineering Recommendations for Resilient Industrial Automation
Industrial teams should evaluate software architecture before consolidating workloads onto shared hardware.
The following practices provide a practical starting point:
- Identify hard real-time, soft real-time, and best-effort workloads.
- Define execution priorities and resource allocation requirements.
- Establish memory and process isolation boundaries.
- Assess cybersecurity requirements using relevant IEC 62443 principles.
- Evaluate functional safety requirements where applicable.
- Test fault recovery, communication failures, and resource exhaustion scenarios.
- Develop a lifecycle maintenance strategy for software components.
Additionally, engineers should verify performance under realistic operating conditions rather than relying exclusively on theoretical processor capacity.
This approach helps identify integration risks before deployment.
The Future of Industrial Automation: Resilience as an Architectural Requirement
Industrial automation is moving toward interconnected, software-defined systems that combine established control technologies with advanced computing.
PLCs and DCS platforms will continue supporting deterministic industrial operations. Meanwhile, MPUs, SoCs, and real-time operating systems will expand the capabilities available at the machine and edge levels.
However, increased computing capacity also creates additional requirements for isolation, cybersecurity, and lifecycle management.
A resilient software foundation provides the architectural structure needed to manage these challenges.
Ultimately, successful industrial modernization requires more than faster processors or additional AI functionality. It requires coordinated engineering across control systems, operating systems, cybersecurity, and operational maintenance.
Manufacturers that address these requirements during system design can introduce new capabilities while maintaining clear boundaries around critical industrial functions.